SBI Data Breach : India’s largest public sector bank, State Bank of India (SBI), is investigating a data exposure incident after nearly 4,000 customer records containing personally identifiable information (PII) were identified in a dataset reportedly found on the dark web.
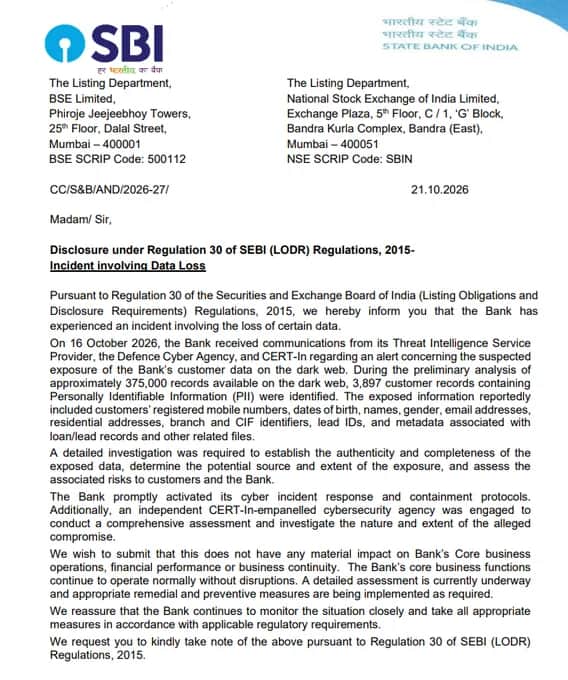
In a recent stock exchange disclosure, the lender stated that a preliminary assessment reviewed approximately 3.75 lakh records and identified 3,897 records containing PII.
According to the bank, alerts regarding the incident were received on October 16, 2026, from its threat intelligence service provider, the Defence Cyber Agency and the Indian Computer Emergency Response Team (CERT-In).
SBI’s response to the data leak
Following the incident, SBI engaged an independent cybersecurity agency empanelled by CERT-In to investigate the matter, establish the source and extent of the data exposure, and assess the associated risks and potential threats.
The information reportedly includes personal details such as names, mobile numbers, email addresses, dates of birth and residential addresses, along with certain customer identifiers and loan-related information.
SBI has stated that the incident has had no material impact on the bank’s core business operations, financial performance or business continuity. The bank is also undertaking remedial and preventive measures to address the incident.
What does this mean for customers?
The exposure of personal information could increase the risk of financial fraud and identity misuse. Potential risks include:
- Targeted phishing attacks: Fraudsters could use personal information to send convincing fraudulent messages or emails.
- Impersonation scams: Criminals could pose as SBI employees and use customers’ personal details to make fraudulent calls appear genuine.
- Misuse of personal information: Exposed data could be combined with information from other sources to facilitate identity fraud or targeted scams.
However, the exposure of personal information does not, by itself, establish that customers’ bank accounts have been compromised or that money has been stolen.
What should customers do if they face fraud?
- Call 1930 immediately: Victims of online financial fraud should contact India’s cybercrime helpline as soon as possible. Prompt reporting may help authorities and banks trace and potentially freeze the defrauded funds.
- Contact the bank or payment provider: Report unauthorised transactions through the bank’s official helpline or app. Request the blocking of affected cards, UPI services or banking access, where necessary.
- File a cybercrime complaint: Visit the National Cyber Crime Reporting Portal and submit the relevant transaction details, payment receipts and supporting evidence. Follow the instructions provided by the helpline or portal.
- Secure accounts: Change compromised passwords using a trusted device, block exposed cards and revoke suspicious login sessions. If a SIM card or email account has been compromised, contact the relevant service provider.
- Preserve evidence: Keep screenshots, bank alerts, transaction IDs, UPI details, suspicious phone numbers, messages and complaint acknowledgement numbers. These may assist the investigation.
Customers should also avoid sharing OTPs, PINs or passwords with anyone claiming to represent a bank or law enforcement agency.
"SBI Data Breach : India’s largest public sector bank, State Bank of India (SBI), is investigating a data exposure incident after nearly 4,00…"